What is ABAC?
Product overview: ABAC
Attribute-based access control is an authorization model that evaluates attributes (or characteristics), rather than roles, to determine access.
The purpose of ABAC is to allow users to define more complex access-control rules to prevent other users from unauthorized actions — those that don't have "approved" characteristics as defined by an organization's security policies.
A simple example of an ABAC rule
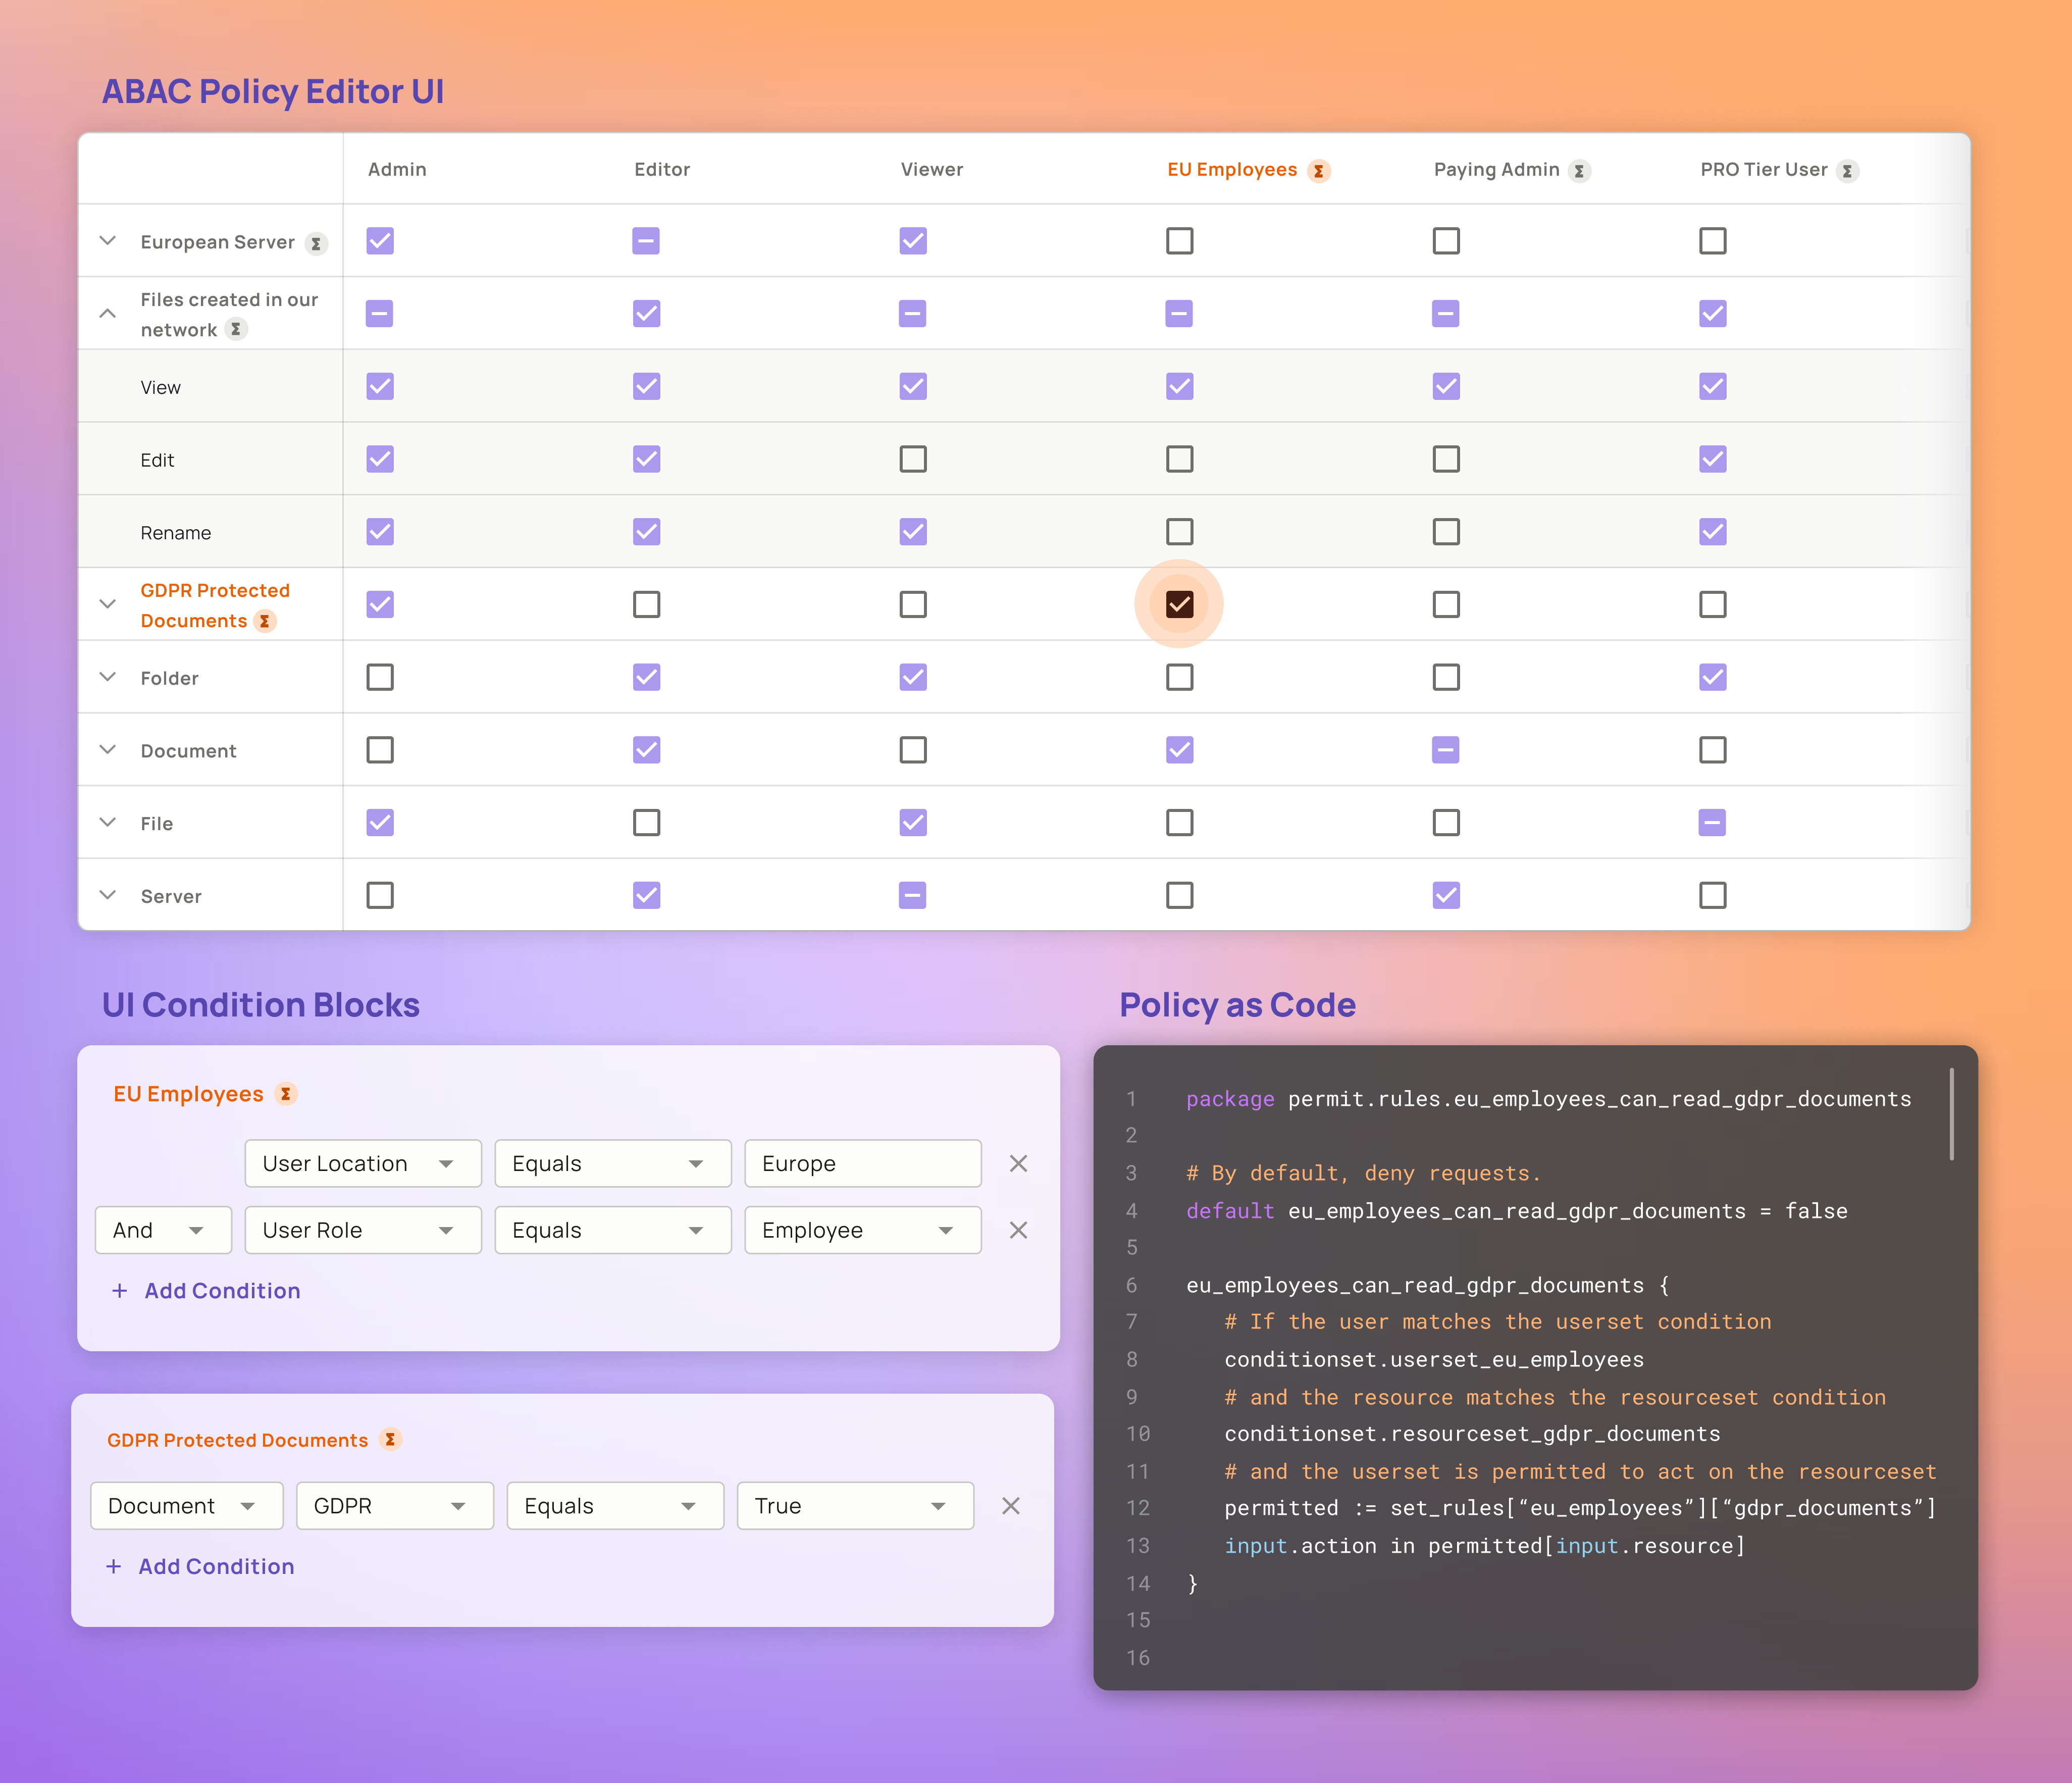
Employees that are based within the European Union can perform any action on GDPR Protected Document.
Fun fact
NIST formalized ABAC's terminology and design considerations in Special Publication 800-162, "Guide to Attribute Based Access Control (ABAC) Definition and Considerations," first published in January 2014. Read the NIST SP 800-162 publication page.